Attackers have stopped relying on a single phishing email. Today's most effective social engineering campaigns move across channels, mixing a convincing email with a phone call to the help desk or a message on a collaboration app, and they use AI-generated voices and faces to sound like someone your team already trusts. Most security programs were built to test one channel at a time, so they rarely see these attacks coming until something has already been reset, approved or paid.
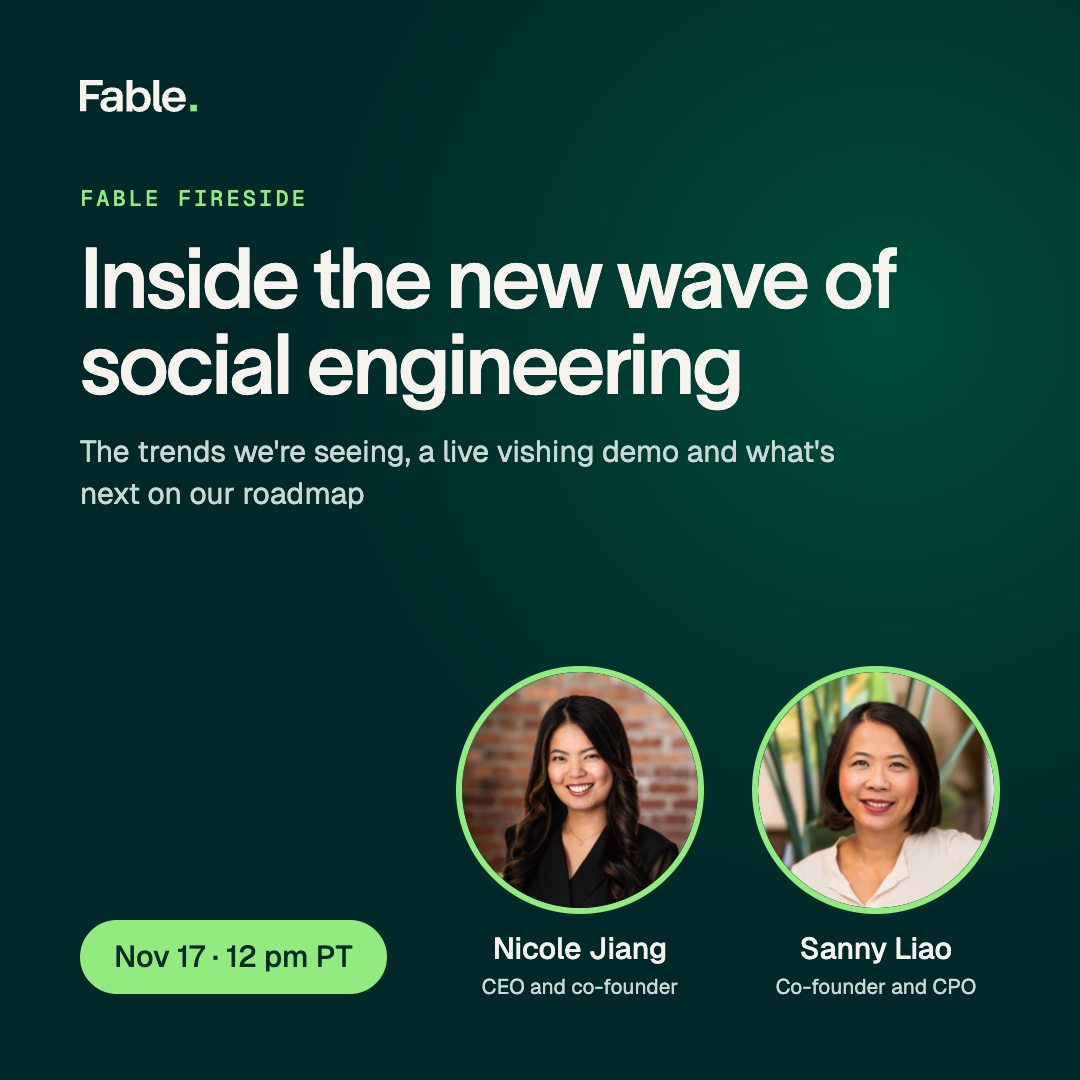
Join Fable co-founders Nicole Jiang and Sanny Liao for a candid, founder-led conversation about what they're seeing across Fable customers and the wider threat landscape, and what security teams can do about it today. They'll show you a live vishing simulation against a help desk line, walk through how Fable turns the result into targeted follow-up and measurable behavior change, and share where they're taking the platform next.
What you'll learn
- The trends behind today's attacks: how attackers are chaining email, voice and chat together, and why the help desk has become one of the easiest ways into a company.
- A live vishing simulation: what it looks like when an authorized deepfake voice calls your service desk, and the transcript and evidence that come back.
- The Fable closed loop in action: how Fable detects risky behavior, intervenes with the right people in the flow of work, and proves that behavior actually changed, so a failed test leads somewhere instead of sitting in a report.
- The roadmap: where Nicole and Sanny are taking Fable next as AI-driven impersonation keeps evolving, and how security teams can prepare.
- Live Q&A: bring your questions about social engineering, deepfakes and human risk, and the founders will answer them on air.