What’s new
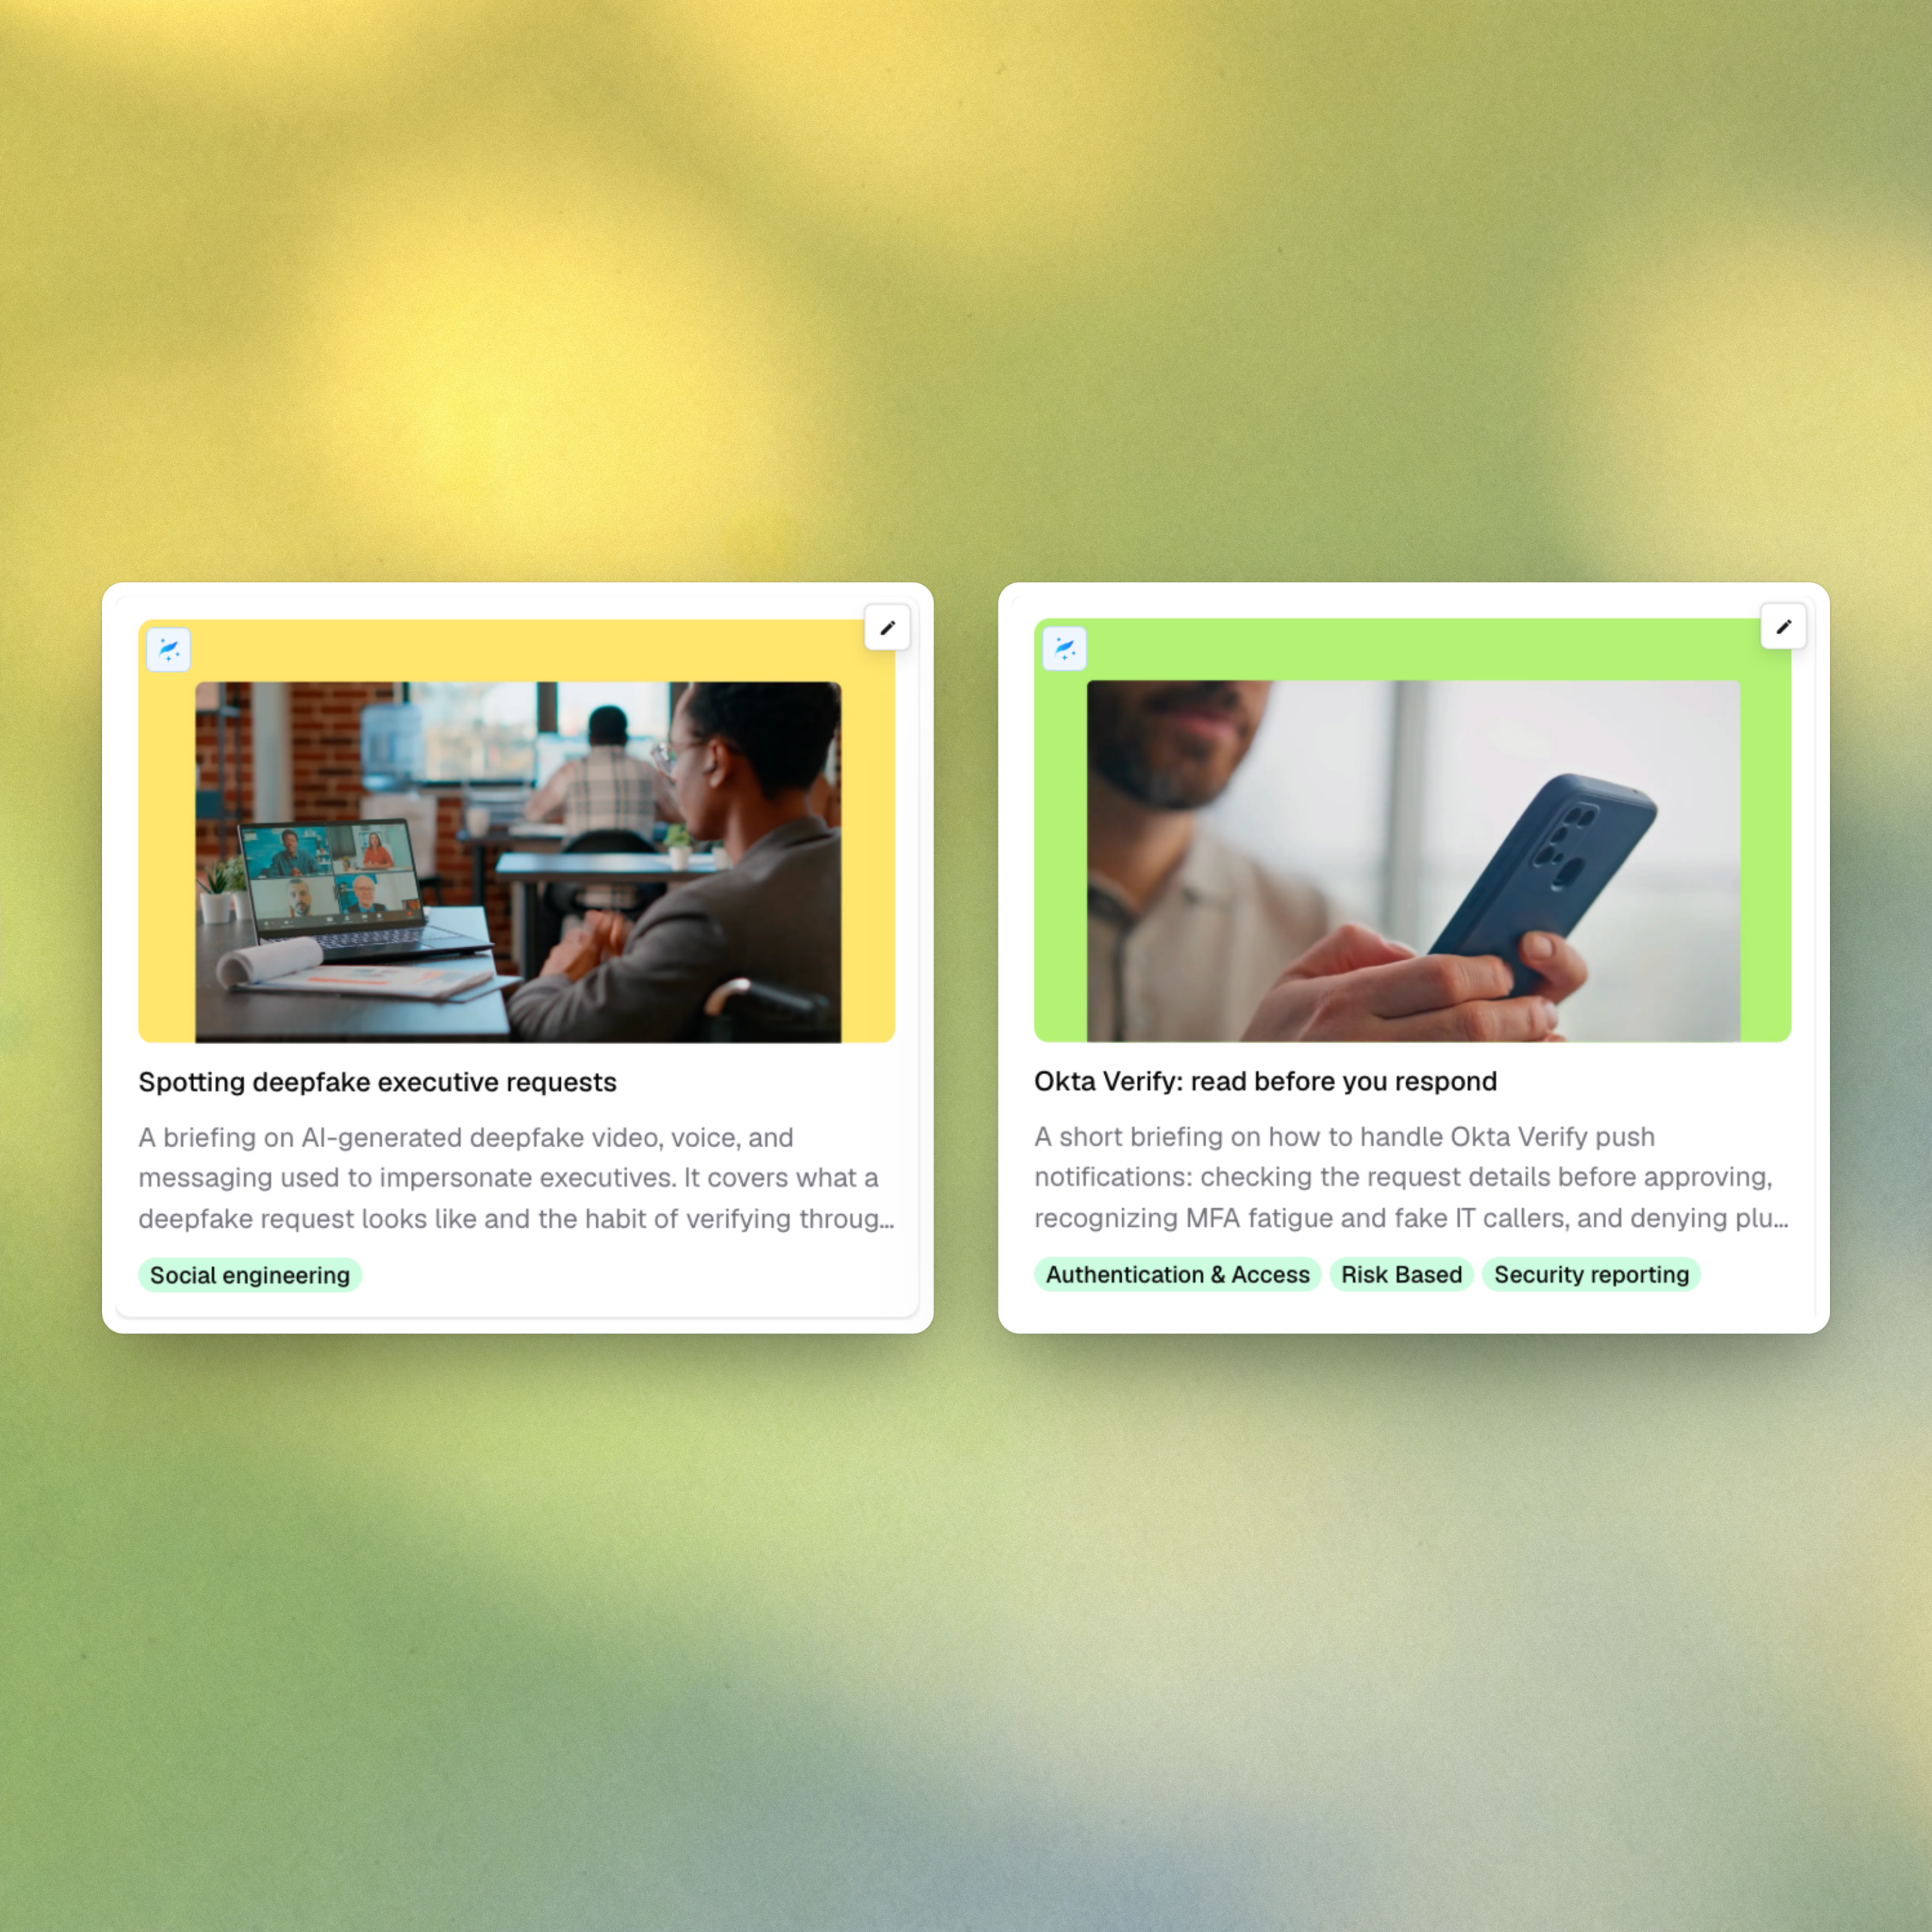
- Spotting deepfake executive requests: A briefing on how attackers impersonate leaders with AI, from live calls with same-day deadlines to follow-up emails with payment links. It covers the authority-plus-urgency pattern and why verifying beats spotting visual glitches.
- Okta Verify: read before you respond: A briefing on handling push notifications. It covers push bombing, fake IT callers asking you to approve a prompt, and the request details to check before approving.
Why it matters
Deepfakes bypass email filters and target trust. The habit that stops them is to pause, call the executive back on a known number, and follow normal approval steps.
Push bombing usually means an attacker already has the password. This briefing reduces every prompt to one question: did I just try to sign in? If not, deny it and report it.
How to access it: These briefings are available in the Fable content catalog. Navigate to the Catalog in the Fable platform to find and deploy them.