

Two new briefings cover attacks that hide inside trusted tools. The first is a Teams chat from “IT Help Desk,” followed by a call asking for remote access. The second is an AI coding assistant recommending a malicious package.
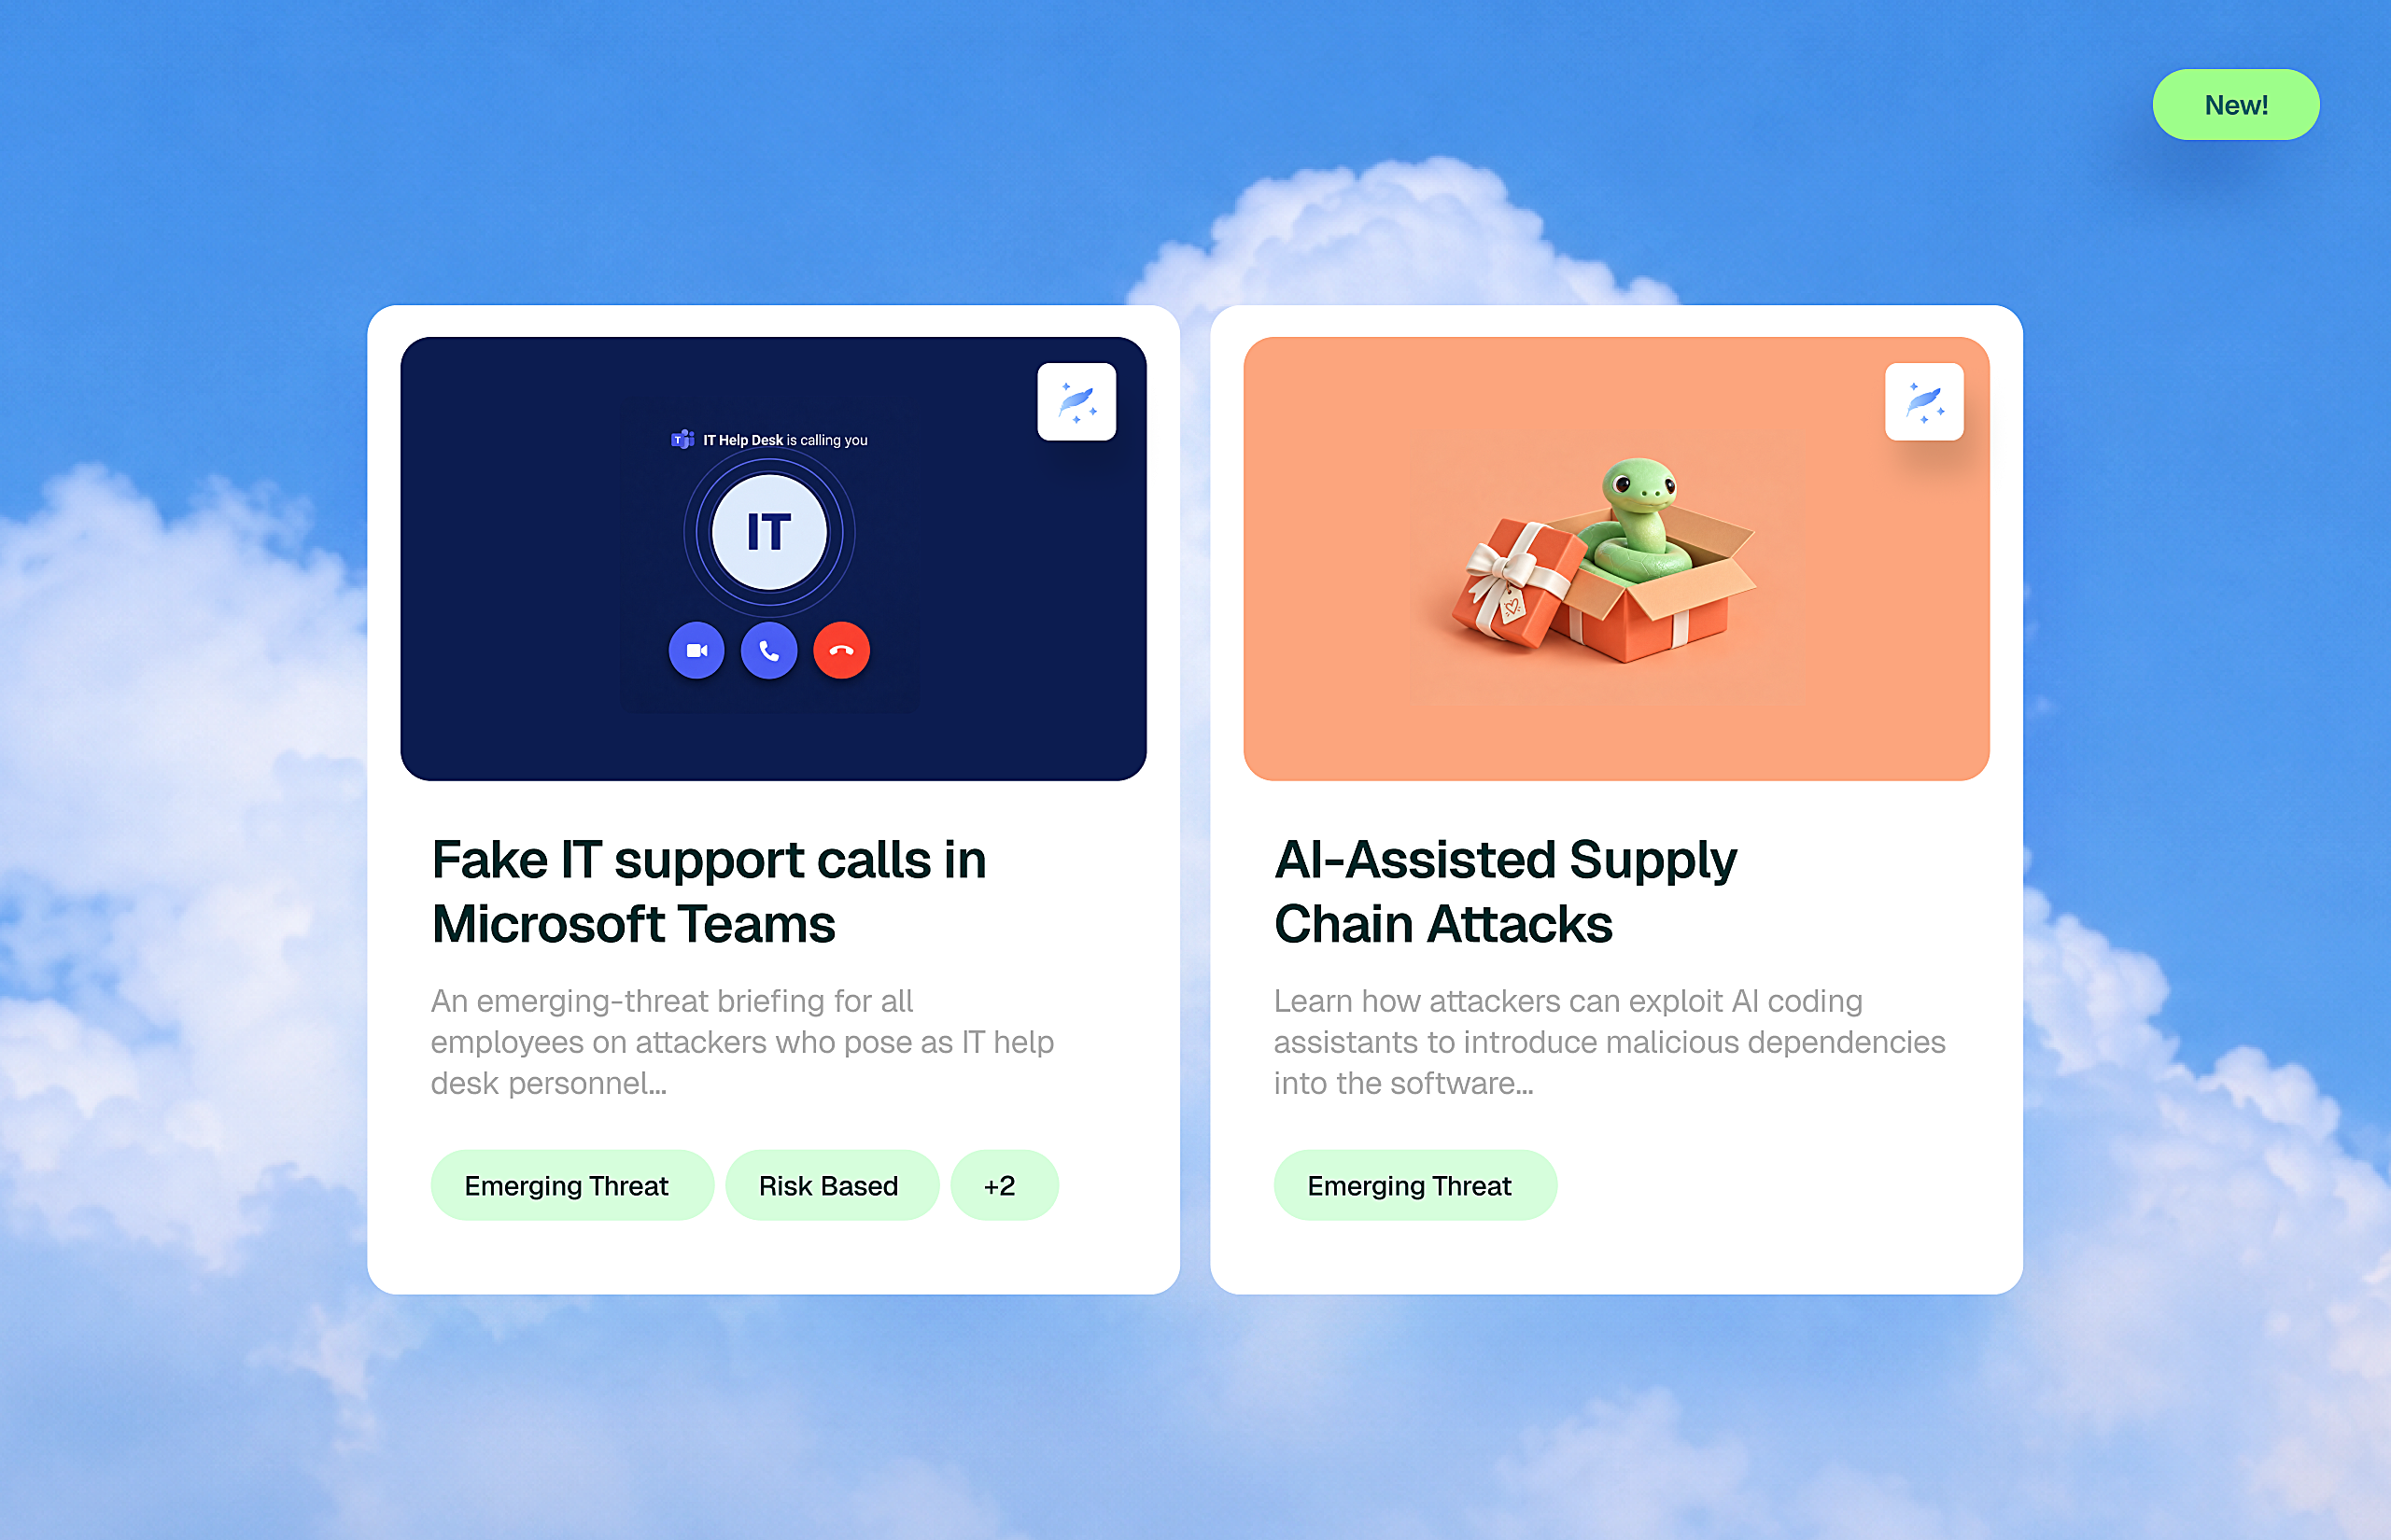
Two new briefings cover attacks that hide inside trusted tools. The first is a Teams chat from “IT Help Desk,” followed by a call asking for remote access. The second is an AI coding assistant recommending a malicious package.
Collaboration tools now account for 42% of phishing alerts, and there’s no link or sender domain to inspect. The habit that stops it: real IT doesn’t call out of nowhere asking for access. Verify through the official help desk, then report.
AI coding assistants often have the same permissions as the developer using them. In one attack, a single poisoned package led to stolen GitHub tokens and a worm spreading across about 100 internal repositories. The rule: treat AI recommendations as suggestions, not trusted instructions.
How to access it: These briefings are available in the Fable content catalog. Navigate to the Catalog in the Fable platform to find and deploy them.